 Talk to usTalk to us
Announcements, releases and milestones from across the platform.
Schneider Electric has disclosed a CVSS 9.8 authentication-algorithm flaw in Modicon M580 and M580 Safety controllers, and remediating it needs both a firmware update and a raised application level.
Advantech's UNO-2484V3 puts a 15 W Arrow Lake-U Core Ultra with up to 14 cores, 64 GB of DDR5, four M.2 slots and three 2.5GbE ports into a fanless −20 to 60 °C enclosure.
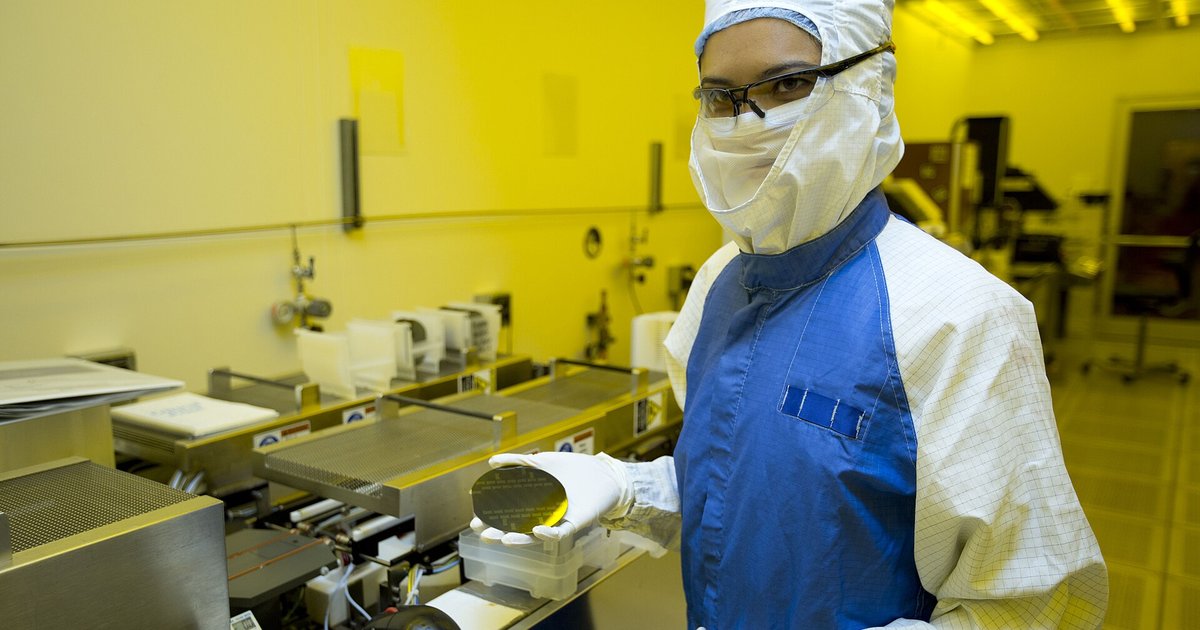
ADI is paying $1.35 billion in cash plus up to $200 million contingent for Alif Semiconductor, whose AI-native microcontrollers pair Arm cores with dedicated low-power neural processing units.
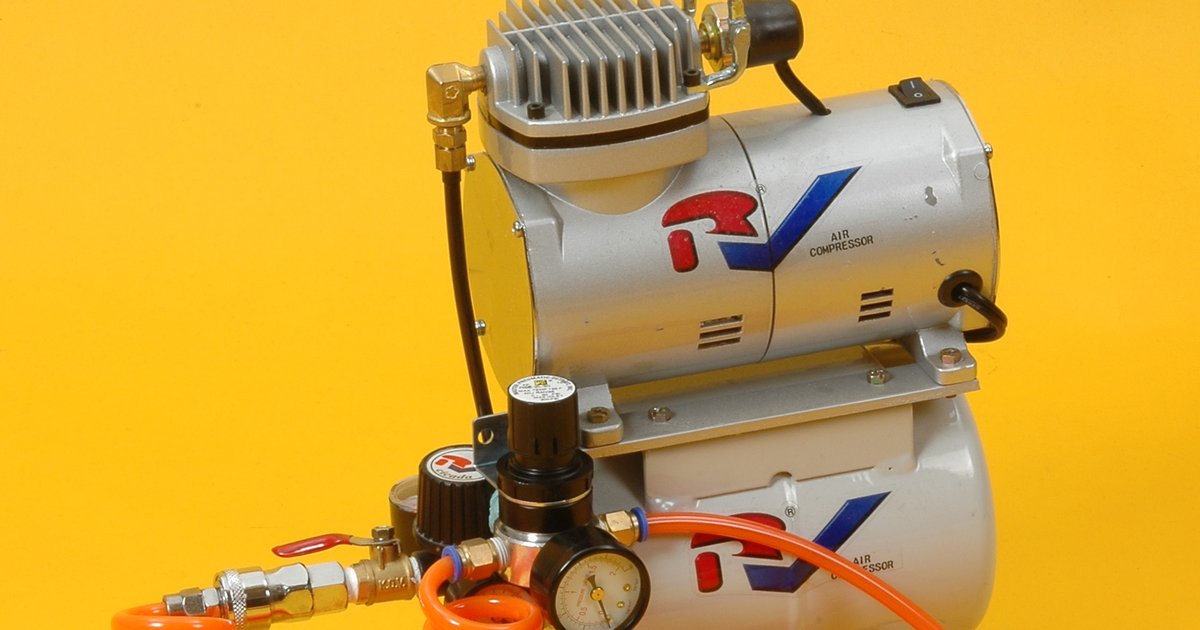
Fluke's ii01 puts acoustic imaging from 2 kHz to 48 kHz into a 50-gram USB-C accessory for Android, with a dedicated compressed-air leak mode and a decibel reading at the target point.
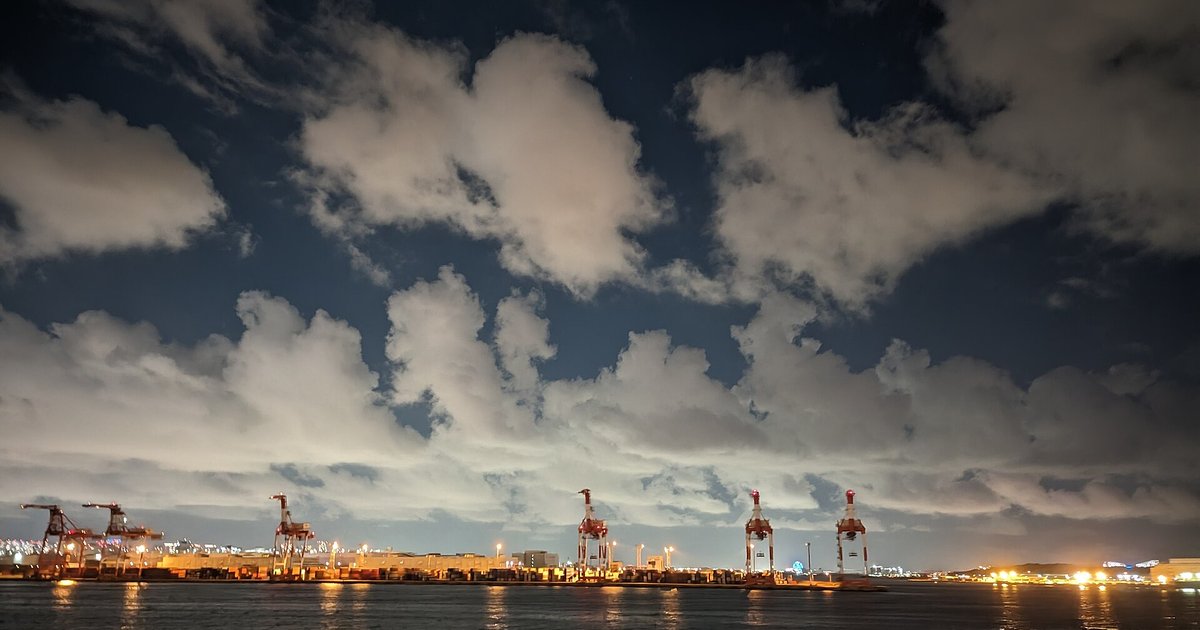
Deutsche Telekom and Ericsson have built a private 5G campus network over HHLA's Container Terminal Altenwerder in Hamburg, covering one square kilometre on 3.7–3.8 GHz.
Wirepas RF mesh now connects close to a million Polaris smart meters in rural Uttar Pradesh, part of more than 11 million meters running the technology across India's national metering programme.
Telit Cinterion is putting a LiteRT runtime on the application cores of its 4G, 5G RedCap and 5G modules, running image classification at no more than 17 percent CPU with no added accelerator.
Renesas has launched the RZ/G3L and RZ/G3SE, quad- and dual-core A55 parts rated −40 to +125 °C with about 1 mW standby, dual TSN-capable gigabit Ethernet and three CAN FD ports, from $14.28.
Stadtwerke Landsberg had its central IT network encrypted overnight on 1 September. Electricity and water kept flowing; the office systems did not, and customer bank details may have been taken.
CERT Polska reports active exploitation of MikroTik RouterOS, including an SSH authentication bypass and a privilege escalation both scored 9.2, with attacks traced to a single address since 2 September.
CISA's advisory on AVEVA Pipeline Integrity Monitor lists a hard-coded cryptographic key, a broken algorithm, a missing authorisation check and a stored XSS — and the fix requires a one-way project file migration.
Siemens has patched a CVSS 9.1 flaw in Industrial Edge Management that lets an unauthenticated attacker complete a password reset for any account without ever receiving the verification link.
Tell us what you're building and we'll help you scope the first deployment.